DPDP Act 2023: ₹250 Crore Penalty — Is Your Company Already at Risk?
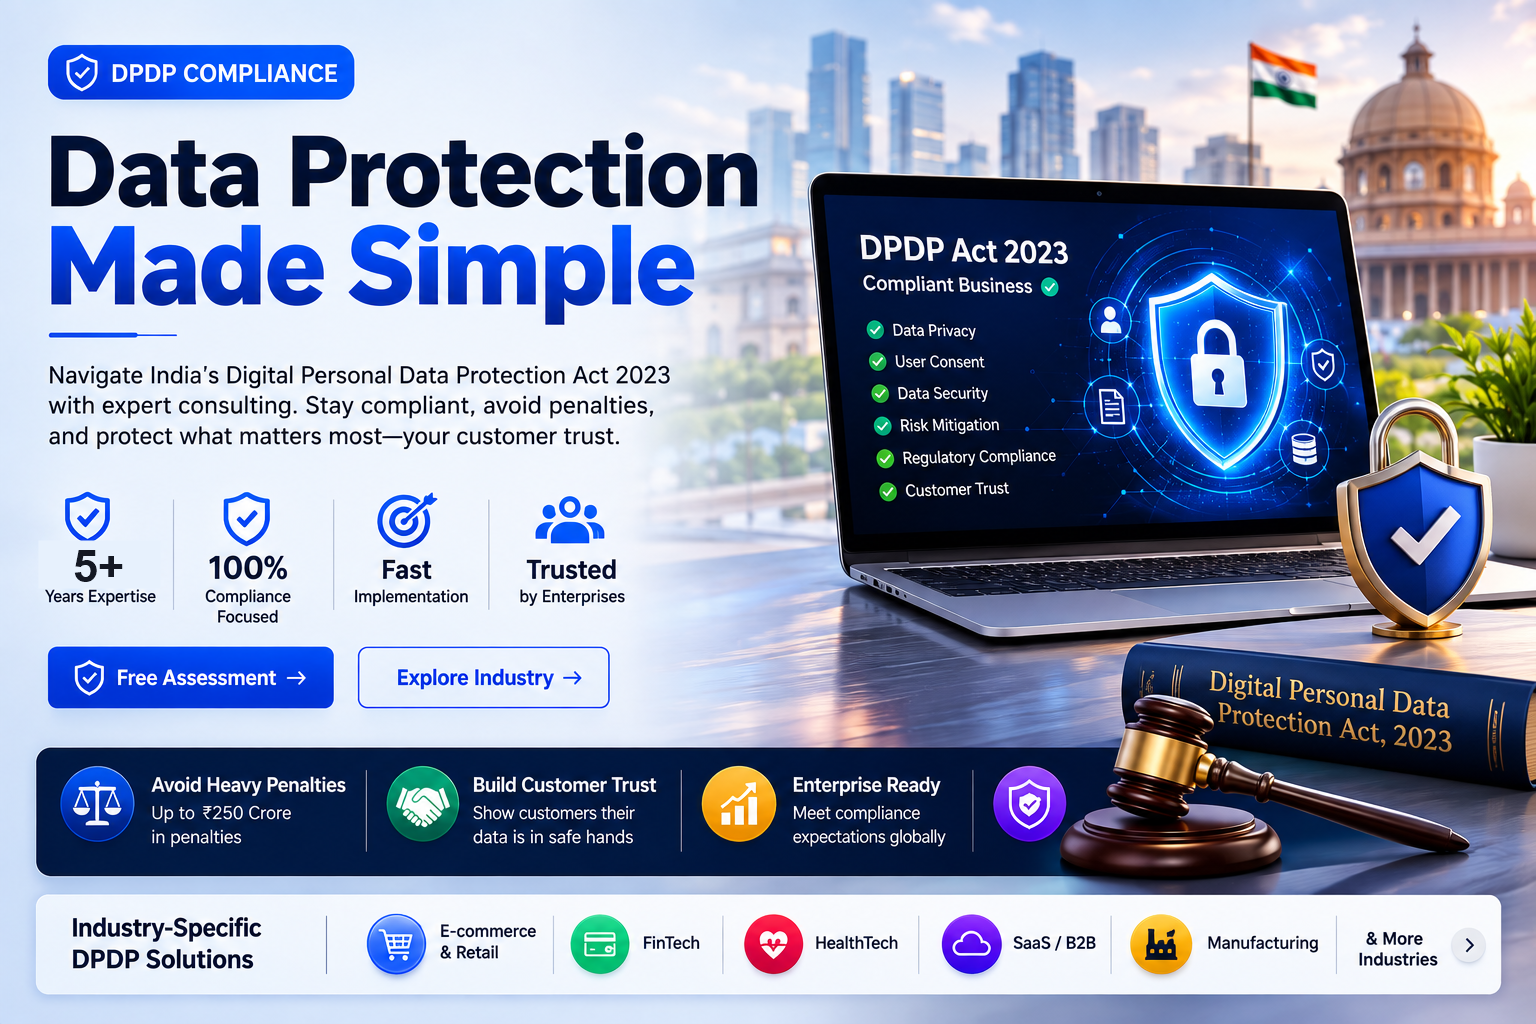
If your business collects even basic customer details — a name, a phone number, an email ID, or an address — you are already covered by India's new data protection law. And if you get it wrong, the fine can go up to ₹250 crore.
This is not a future problem. The Digital Personal Data Protection Act, 2023 (DPDP Act) is now backed by the DPDP Rules 2025, and enforcement is rolling out in phases through May 2027. Many businesses still think this law is "for big tech companies only." That belief is wrong, and it is an expensive mistake to make.
This guide breaks down the DPDP Act 2023 in plain words: what the ₹250 crore penalty actually means, who has to follow the law, what the full penalty list looks like, and the exact steps you can take today to protect your business.
Quick Answer: What Is the ₹250 Crore DPDP Penalty?
The ₹250 crore penalty is the highest fine under the DPDP Act 2023. It applies when a company (called a "Data Fiduciary" under the law) fails to put in place reasonable security measures and this failure leads to a personal data breach.
Unlike Europe's GDPR, which fines companies as a percentage of yearly turnover, India's law sets a fixed maximum rupee amount for each type of violation. That means even a small or mid-sized company can be fined the same maximum amount as a giant corporation, based purely on how serious the violation is — not on how much money the company makes.
What Is the DPDP Act 2023, in Simple Words?
The Digital Personal Data Protection Act, 2023 is India's first full law on how companies must handle people's personal data. It became law after getting presidential approval in August 2023.
In simple terms, the law says:
• If you collect personal data from people in India (names, phone numbers, health details, financial info, location data, and more), you have rules to follow. • People whose data you collect (called "Data Principals") have rights — like the right to know what data you have, the right to ask you to fix wrong data, and the right to ask you to delete it. • If you fail to protect this data properly, or you misuse it, the government can fine you.
Does the Law Apply to Foreign Companies Too?
Yes. This is one of the most misunderstood parts of the DPDP Act. The law has "extra-territorial application." If you offer products or services to people located in India and you process their personal data as part of that, you must follow this law. A U.S.-based SaaS company with Indian customers is just as much on the hook as a company based in Mumbai.
DPDP Act Timeline: From Bill to Enforcement
Understanding the timeline matters because it tells you exactly how much time you have left.
Key Dates:
- August 11, 2023: DPDP Act passed and received presidential assent
- November 13-14, 2025: DPDP Rules 2025 notified (operational rules released)
- May 13, 2027: Full compliance deadline
The big misunderstanding: many businesses believe "2027" means they have two more years to relax. In reality, the DPDP Rules already require you to build your systems, policies, and internal processes now, well before the enforcement deadline arrives.
The Full DPDP Act Penalty Schedule
The DPDP Act doesn't have just one fine. It has a full schedule of penalties depending on what rule you break:
| Violation | Maximum Penalty |
|---|---|
| Failure to take reasonable security safeguards, leading to a data breach | ₹250 crore |
| Failure to notify the Board and affected users about a data breach | Up to ₹200 crore |
| Non-compliance with obligations related to children's personal data | Up to ₹200 crore |
| Non-compliance with additional obligations of a Significant Data Fiduciary | Up to ₹150 crore |
| General non-compliance with other obligations under the Act | Up to ₹50 crore |
| Breach of duties by a Data Principal (individual misuse of the system) | Up to ₹10,000 |
For a detailed breakdown of each penalty, see DPDP Penalties Explained.
A few things to notice from this table:
- The penalties are per instance, not per year. One serious incident that breaks multiple rules at once can rack up several penalties stacked together.
- Individuals face tiny fines; companies face huge ones. Companies face the crore-level fines.
- The Board decides the exact amount. These are maximum caps, not fixed amounts.
Why the ₹250 Crore Fine Specifically Targets Security Failures
The single highest penalty under the entire Act — ₹250 crore — is reserved for one specific failure: not having "reasonable security safeguards" in place, which then leads to a personal data breach.
Learn more about DPDP compliance requirements to build a robust security framework.
This tells you something important about how lawmakers see risk: weak security is treated as the most dangerous failure a company can commit. The logic is simple. A data breach can expose thousands or millions of people's personal information at once — financial records, health data, home addresses, family details. The damage from a single breach can ripple out far beyond the company that caused it.
What Counts as "Reasonable Security Safeguards"?
Under Rule 6 of the DPDP Rules 2025, reasonable security safeguards include:
• Data encryption • Access controls that limit who can view sensitive data • Ongoing monitoring and logging of data access • Secure backups and cloud storage • Security measures for third-party tools
In plain terms, your customer database shouldn't be sitting unprotected on an open server. Only employees who genuinely need access to sensitive data should have it.
The Hidden Risk: You're Liable for Your Vendors Too
Here is the part of the DPDP Act that catches the most companies off guard: you are responsible even when the mistake is your vendor's fault.
Under the DPDP Act, a Data Fiduciary (your company, if you decide why and how personal data is processed) remains "vicariously liable" for any data breach caused by a Data Processor (a third party you hired, like a cloud hosting company, a CRM tool, or a marketing agency).
Real-world example: Imagine your company hires a third-party marketing platform to manage your customer email list. That platform gets hacked, and your customers' data leaks. Under the DPDP Act, your company — not just the marketing platform — can be held responsible and fined, because the platform was processing data on your behalf.
For guidance on data processor agreements and vendor management, see our complete guide.
This is why simply hiring "trusted vendors" is not enough anymore. You need contracts, security checks, and ongoing oversight of every processor that touches your customers' data.
Who Enforces the DPDP Act? Meet the Data Protection Board
The Data Protection Board of India (DPBI) is the body that actually investigates complaints, runs inquiries, and decides penalties. The Board takes a risk-based approach, meaning it looks at several factors before setting a fine:
• The nature of the company — a bank handling financial data is judged differently than a small e-commerce store. • The volume and sensitivity of data involved — a breach affecting a few hundred people is treated differently than one affecting millions, or one involving health records. • The harm caused to individuals — did people lose money, face identity theft, or suffer emotional distress? • How long the violation lasted — a quickly-fixed mistake is judged more leniently than a problem that went unnoticed for months.
Importantly, a company's response after a breach also matters. The Board considers mitigating factors such as self-disclosure, quick remediation, cooperation with investigators, and a track record of prior compliance. In plain words: owning up to a mistake quickly and having your compliance paperwork in order can genuinely reduce your fine.
Why "We're Too Small to Be a Target" Is a Dangerous Myth
A lot of small and mid-sized businesses assume data protection laws are only a concern for large corporations like banks or tech giants. This is one of the most common — and costly — misunderstandings about the DPDP Act.
Consider these facts:
• Cybersecurity incidents in India more than doubled between 2022 and 2024. Smaller businesses are frequently the easier targets because they often have weaker defenses. • The law's scope applies regardless of a company's turnover or financial status. There is no "small business exemption" written into the law for the core obligations. • India's digital economy is projected to become a one-trillion-dollar market, with over 900 million internet users already online. More digital activity means more personal data flowing through more companies — and more scrutiny.
If your business runs an e-commerce store, a SaaS product, a healthcare app, a fintech tool, or even a simple lead-generation website that collects names and phone numbers, you are collecting personal data. That alone puts you inside the scope of this law.
A Realistic Scenario: How a Small Mistake Turns Into a Penalty
To understand how this plays out in real life, consider a common situation:
An e-commerce app has a generic privacy policy that simply says it collects information "to improve user experience." It doesn't clearly explain that it also uses purchase history to run targeted ads. A customer notices this, feels misled, and files a complaint. The Board investigates and finds that the notice given to customers was too vague to count as valid consent.
This single oversight — a vague privacy notice — can be treated as processing data without proper consent, which is a major violation. Depending on severity, this kind of failure alone can lead to penalties up to ₹200 crore, on top of reputational damage that's harder to put a number on.
The lesson here isn't really about privacy policies specifically. It's that small, boilerplate mistakes that seem harmless on the surface can trigger some of the largest penalties under this law.
7-Step DPDP Compliance Checklist for Your Business
Based on the core compliance domains that legal and audit experts map to the DPDP Act and DPDP Rules 2025, here is a practical roadmap you can start working through right now.
1. Build Your Governance Structure
Assign clear accountability inside your company for data protection. If you qualify as a "Significant Data Fiduciary" (a category for companies handling large volumes or highly sensitive data), you'll need to appoint a Data Protection Officer and an independent auditor.
2. Map Your Data
Know exactly what personal data you collect, where it's stored, why you collect it, and what legal basis you have for processing it. You cannot protect data you haven't inventoried.
3. Fix Your Notice and Consent Process
Your privacy notice must clearly describe what data you collect and exactly why, using specific, itemized language — not vague phrases like "to improve services." Consent must be freely given, specific, informed, and just as easy to withdraw as it was to give.
4. Set Up Data Principal Rights Handling
Build a simple process that lets people access their data, request corrections, ask for deletion, and file grievances. This includes designating a specific contact person who can answer questions about how you handle data.
5. Strengthen Security Safeguards
Put in place encryption, access controls, and activity logging. Remember, this is the area tied to the ₹250 crore penalty, so it deserves the most attention and investment.
6. Prepare a Breach Response Plan
Have a clear, tested plan for detecting a data breach and reporting it to both the Data Protection Board and affected individuals within the required timelines. A slow or missing breach notification can add a separate ₹200 crore penalty on top of everything else.
7. Review Your Vendor Contracts
Since your company remains liable for data breaches caused by third-party processors, review every vendor contract. Make sure your data processors are contractually required to meet the same security standards you follow internally.
Cross-Border Data and Children's Data: Two Areas Companies Often Miss
Two specific areas of the DPDP Rules 2025 deserve special mention because they're easy to overlook:
Cross-border data transfer: If your company sends Indian users' personal data outside India — for example, to a cloud server in another country — the DPDP Rules set specific standards for how this must be handled. This matters a lot for global SaaS companies and outsourcing businesses.
Children's data: The Act requires "verifiable consent" before processing data belonging to children, meaning you can't simply assume a person is an adult based on a checkbox. Getting this wrong can trigger penalties up to ₹200 crore.
Frequently Asked Questions About the DPDP Act 2023
What is the maximum penalty under the DPDP Act 2023? The maximum penalty is ₹250 crore per instance, applied when a company fails to implement reasonable security safeguards and this failure results in a personal data breach.
When does the DPDP Act become fully enforceable? The final compliance deadline is May 13, 2027, though core obligations around consent, security, and breach reporting become active well before the final deadline.
Does the DPDP Act apply to companies outside India? Yes. Any company anywhere in the world that offers goods or services to people located in India, and processes their personal data as part of that, must comply with the DPDP Act.
Is my company liable if a third-party vendor causes a data breach? Yes. Under the DPDP Act, your company (the Data Fiduciary) remains responsible for breaches caused by a Data Processor working on your behalf, even if the fault technically lies with that third party.
Who decides how much a company gets fined? The Data Protection Board of India investigates complaints and decides penalty amounts, considering factors like the seriousness of the violation, the sensitivity of the data involved, the harm caused, and how the company responded after the incident.
Are DPDP Act penalties based on company revenue, like GDPR? No. Unlike the GDPR, which calculates fines as a percentage of a company's global turnover, the DPDP Act sets fixed maximum rupee amounts for each type of violation, regardless of company size.
The Bottom Line: Don't Wait for a Complaint to Find Out You're Exposed
The DPDP Act 2023 is not a distant regulation aimed only at big corporations. It applies to nearly every business that collects even basic personal information from people in India — and the ₹250 crore penalty is designed specifically to punish companies that treat data security as an afterthought.
The good news is that compliance is achievable, and it doesn't require overhauling your entire business overnight. It requires a clear-eyed look at what data you collect, how you protect it, and how well your vendors are protecting it on your behalf.
If you're unsure where your business currently stands, Cor Advance Solutions' DPDP compliance service can help you assess your risk and build a practical, step-by-step plan to get compliant before enforcement catches up with you.
Ready to ensure your business is DPDP compliant?